Trezor has significantly reduced its reseller network after uncovering malicious implants in its hardware wallets that could compromise cryptocurrency recovery phrases. The company has released a firmware update to block these implants but warns affected users to create new wall…
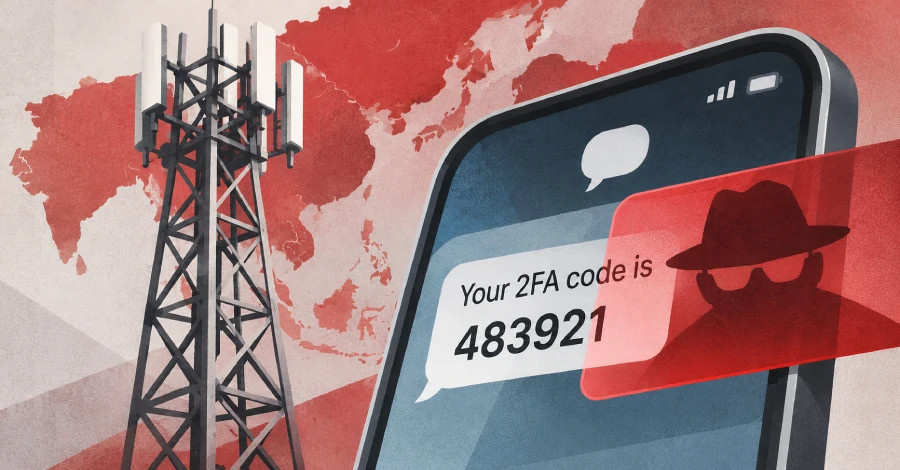
Telecom security firm Enea has published findings on two threat actors, SilentAir and LIMINAL PANDA, who are infiltrating mobile networks to spy on users and intercept communicati…
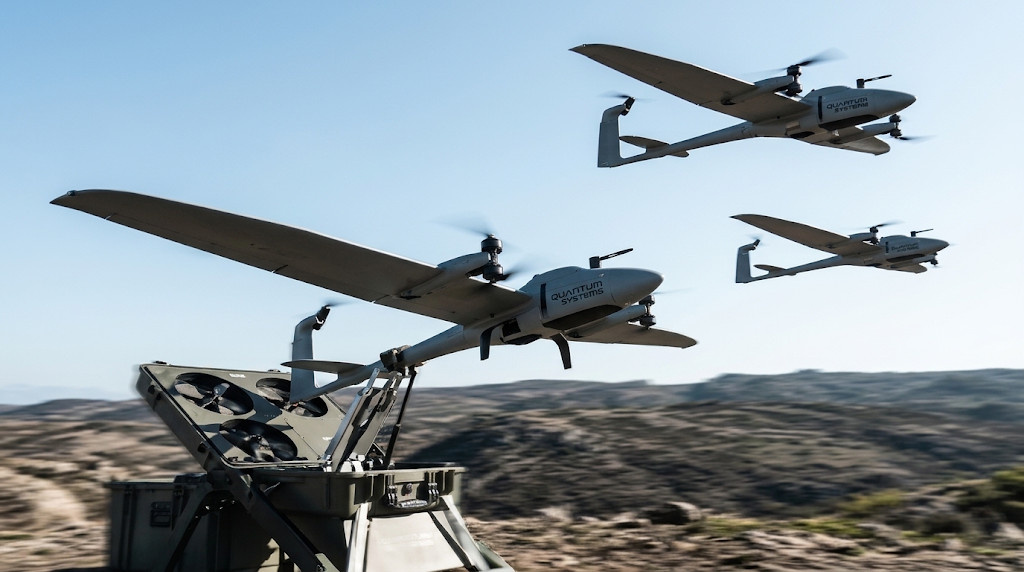
Quantum Systems, a German defense contractor, confirmed a cyberattack that disrupted its drone operations. The company reported that its security teams contained the threat and ar…
Cursor has confirmed a security breach that enabled hackers to distribute a malicious version of the Claude Code extension through its marketplace. The breach occurred after attac…
A recently discovered espionage group, SilentAir, has been utilizing compromised equipment within Asian mobile operators to intercept calls and text messages, particularly affecti…
A serving Indian Air Force Wing Commander has been accused of leaking sensitive military information, including details about India's war plans and drone capabilities, to a Pakist…
Recent research has identified three distinct espionage campaigns linked to China, targeting telecommunications, government, and military sectors across Latin America, Asia, and E…
The Russia-aligned group Turla has utilized a modular .NET toolset, named Cereal, to infiltrate Microsoft Exchange servers at government organizations in Kazakhstan and Romania. T…
The Russian state-sponsored hacking group Turla has been utilizing a new malware toolset named 'Cereal' to intercept emails on Microsoft Exchange servers at various government org…
The Russian state-sponsored hacking group Turla has introduced a new cyber espionage tool named Cereal, designed to infiltrate Microsoft Exchange servers and collect sensitive ema…
Binance, the leading cryptocurrency exchange, has denied allegations of a data breach made by a threat actor claiming to represent the ShinyHunters group. The individual purported…
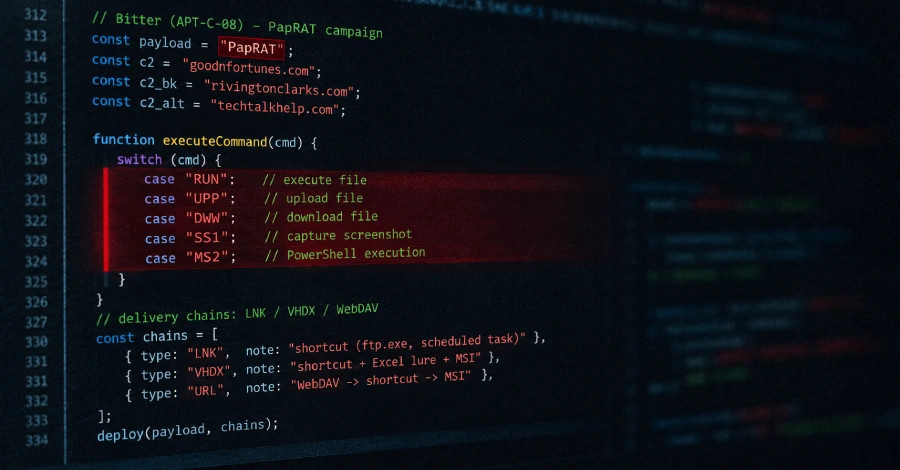
The Bitter hacking group, also known as APT-C-08, has launched a cyber espionage campaign targeting South Asian organizations using a new remote access trojan named PapRAT. This m…
The FBI has issued a warning about a sophisticated scheme by North Korean hackers who exploit stolen webcam recordings to impersonate crypto workers. This tactic not only deceives…
At the recent Proofpoint Protect event, industry experts discussed the evolving role of AI in cybersecurity, emphasizing the need for intent-based governance as AI agents become m…
ESET Research's latest report examines the tactics and tools employed by Gamaredon, a prominent Russia-aligned cyberespionage group, throughout 2025. The analysis highlights the g…
Palo Alto Networks is set to report its earnings on September 1, with Wall Street analysts raising their price targets in anticipation of strong results. The company has seen sign…
 Spook.News