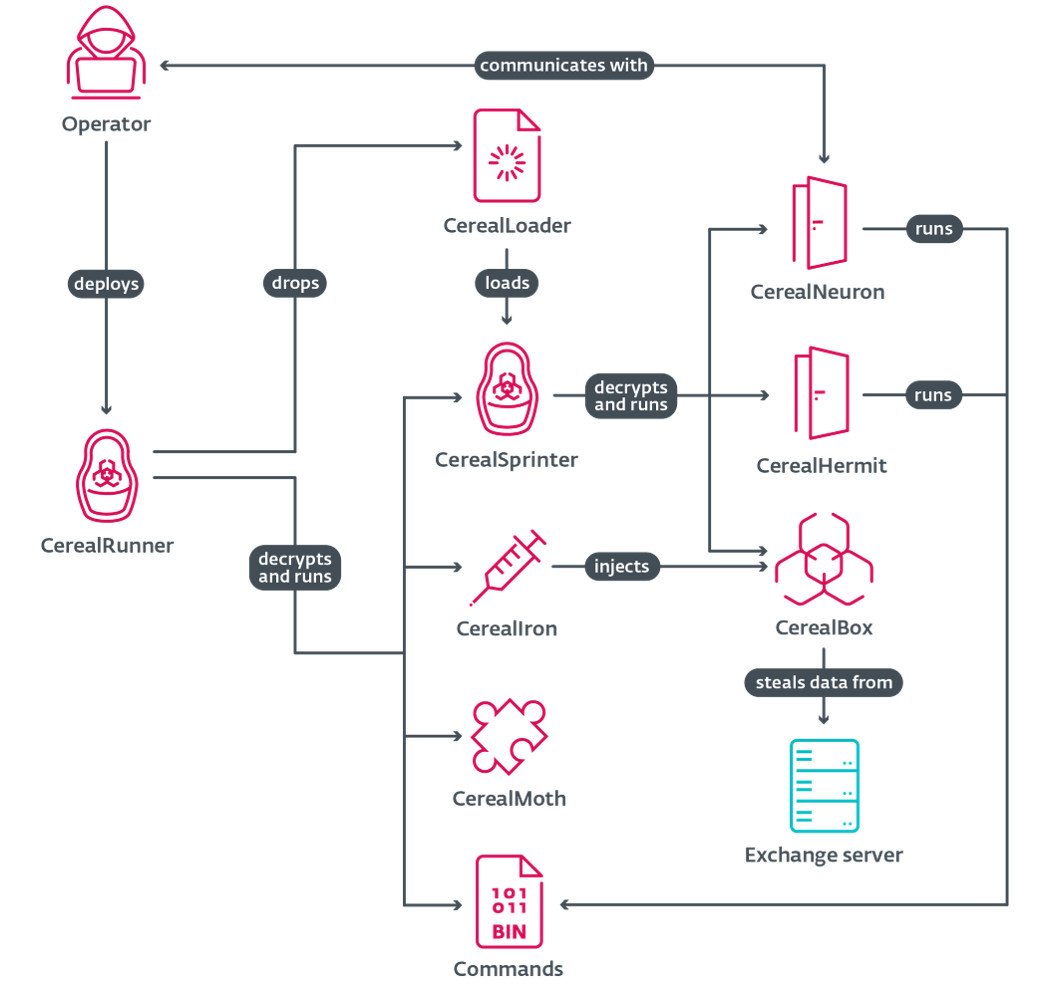
ESET Research has revealed a previously undocumented toolset named Cereal, utilized by the Russian-linked APT group Turla on Microsoft Exchange servers in Kazakhstan and Romania. The toolset, designed for stealthy cyber espionage, allows attackers to monitor communications and e…
The Russia-linked threat group Turla has employed a new toolset named Cereal on compromised Microsoft Exchange servers to target emails associated with NATO and the European Union…
The Russia-aligned group Turla has utilized a modular .NET toolset, named Cereal, to infiltrate Microsoft Exchange servers at government organizations in Kazakhstan and Romania. T…
The Russian state-sponsored hacking group Turla has been utilizing a new malware toolset named 'Cereal' to intercept emails on Microsoft Exchange servers at various government org…
The Russian state-sponsored hacking group Turla has introduced a new cyber espionage tool named Cereal, designed to infiltrate Microsoft Exchange servers and collect sensitive ema…
ESET has identified the Gorbag APT group, aligned with Russian interests, as a significant threat to Ukrainian organizations since early 2025. Utilizing spearphishing tactics and…
The ESET APT Activity Report for Q2 and Q3 2026 details significant activities of various advanced persistent threat (APT) groups. The report highlights operations by China-aligne…
The BlackX UEFI bootkit has been identified as a significant threat in an espionage campaign that began in early 2026. By exploiting the Baton Drop vulnerability, it bypasses Secu…
Russia-linked hackers have utilized the Yggdrasil network to obscure their communications during a cyberattack on a Ukrainian grain logistics company. This incident marks the firs…
ESET researchers have documented the evolution of the MATCHBOIL malware, a custom C# downloader used by the Russia-aligned UAC-0099 APT group. This malware has undergone significa…
A Russia-aligned cyber espionage group known as UAC-0099 has significantly upgraded its MATCHBOIL downloader over the past two years. Recent research indicates that the malware ha…
ESET researchers have traced the evolution of MATCHBOIL, a downloader utilized by the Russia-aligned group UAC-0099 to install a spying backdoor on Windows systems in Ukraine. Thi…
ESET Research's latest report examines the tactics and tools employed by Gamaredon, a prominent Russia-aligned cyberespionage group, throughout 2025. The analysis highlights the g…
 Spook.News