Volt Typhoon Employs Silent Train Relay Network for Cyber Intrusions
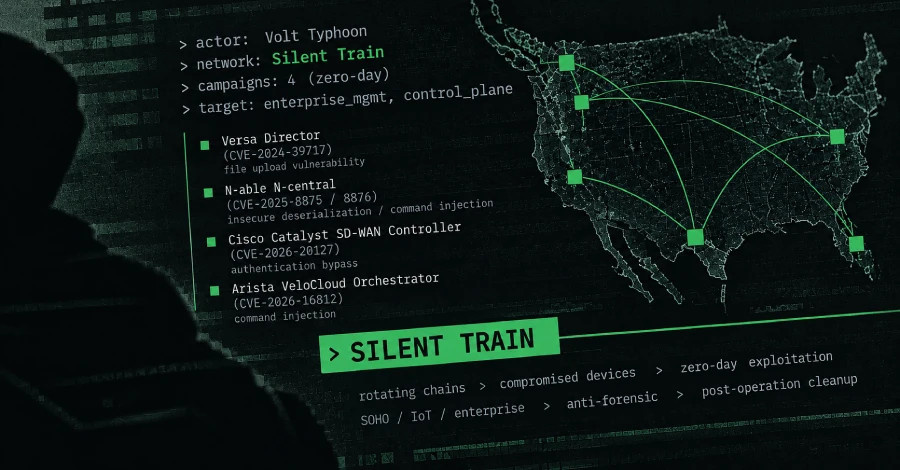
Volt Typhoon, a Chinese state-sponsored advanced persistent threat (APT) group, has been leveraging a covert and constantly rotating relay network to facilitate its cyber espionage efforts against critical infrastructure in the United States. This network, referred to as Silent Train by researchers at Lumen's Black Lotus Labs, consists of chains of compromised small office/home office (SOHO) and Internet of Things (IoT) devices, as well as enterprise systems. These include well-known brands such as TP-Link and Netgear routers, along with Fortinet and Cisco appliances.
The group has exploited zero-day vulnerabilities in various network and endpoint management systems, including SD-WAN orchestrators and other control plane infrastructure. By compromising these technologies, Volt Typhoon has achieved significant operational advantages, allowing them to navigate networks with minimal effort and without leaving substantial forensic evidence behind.
Researchers noted that post-incident analyses revealed the presence of in-memory webshells, credential harvesting, and the manipulation of logs to erase traces of their activities. The Silent Train network has been used to target a wide array of edge, identity, network, and enterprise management technologies, although it remains unclear whether the group exploited known or unknown vulnerabilities.
In a related analysis, Cisco Talos researchers highlighted the overlap between Volt Typhoon's infrastructure and that of another group, UAT-11473, which exploited a specific vulnerability to compromise Cisco SD-WAN Catalyst Controller instances and deploy a custom malware framework known as KeyDrift. This malware allows persistent access to the controllers and facilitates the extraction of sensitive control-session metadata.
Evolution of the Silent Train Network
The Silent Train network was established prior to the takedown of the KV botnet in December 2023 and has seen increased utilization since then. Unlike traditional botnets that rely on persistent infrastructure, Volt Typhoon's approach involves rapidly assembling and dismantling transient networks, creating a resilient framework that conceals their activities.
Over the past three years, Black Lotus Labs has monitored the Silent Train network, leading to numerous victim notifications. The group has been selective in its targeting, often focusing on one to five victims per session, which frequently include U.S. government entities, telecommunications providers, defense contractors, and critical infrastructure organizations in sectors such as energy and transportation.
Intelligence Reviewed
Geographically, the states of Hawaii, California, and Texas have been the most affected, given their significance in military operations and critical infrastructure. This targeting pattern suggests a strategic effort to pre-position access within essential communications and infrastructure networks, particularly in anticipation of geopolitical tensions.
As the Silent Train network evolved, it incorporated reverse-tunnel variants alongside traditional SSH-chaining models, enhancing its operational stealth. This sophisticated approach allows the group to maintain a secure and compartmentalized framework for exploitation and data exfiltration, further complicating detection efforts by cybersecurity defenders.