Iran-linked Mirage Kitten Exploits Fake Job Tests to Distribute Malware
Mirage Kitten, an Iranian APT group, has devised a novel strategy to distribute malware by leveraging fake job tests aimed at software engineers. According to research from Kaspersky, the group sends coding assessments through LinkedIn, instructing candidates not to use AI tools during the review process. This tactic is designed to prevent detection of the malware embedded within the coding challenges.
The process begins when a fake recruiter contacts a potential candidate, offering a job and providing a link to a coding assessment hosted on a seemingly legitimate Amazon S3 link. The assessment includes a README file that imposes a three-hour time limit and explicitly prohibits the use of AI assistants, which would typically flag suspicious code.
Kaspersky's report highlights that the malware, identified as NodeRabbit, is written in Node.js and can operate across multiple operating systems, including Windows, Linux, and macOS. This marks a shift for Mirage Kitten, which has previously relied on malware written in C, C++, and Go. NodeRabbit is concealed within a fake npm package included in the coding test, and once executed, it establishes a connection to a command server using AES-256-GCM encryption.
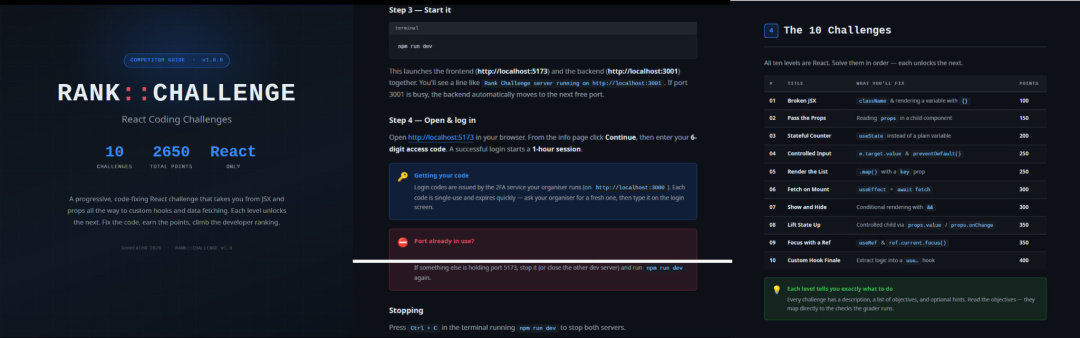
In addition to NodeRabbit, Kaspersky discovered another malware family named PollCat, which is disguised as a React coding challenge. This malware requires candidates to enter a six-digit access code provided by the recruiter, creating a sense of urgency that discourages thorough scrutiny of the code.
Both malware families have been linked to Mirage Kitten with high confidence, as researchers found similarities in their network code and behavior. Victims of these attacks have primarily been identified in the fintech and aviation sectors across Egypt, Ethiopia, and Afghanistan, aligning with the group's historical targeting patterns in the Middle East and Africa.
This development underscores the evolving tactics of Mirage Kitten, as they adapt their methods to exploit legitimate job-seeking processes. Organizations that conduct hiring through LinkedIn and utilize coding assessments should be vigilant, as these attacks are not characterized by suspicious emails but rather by seemingly normal job opportunities with legitimate download links.