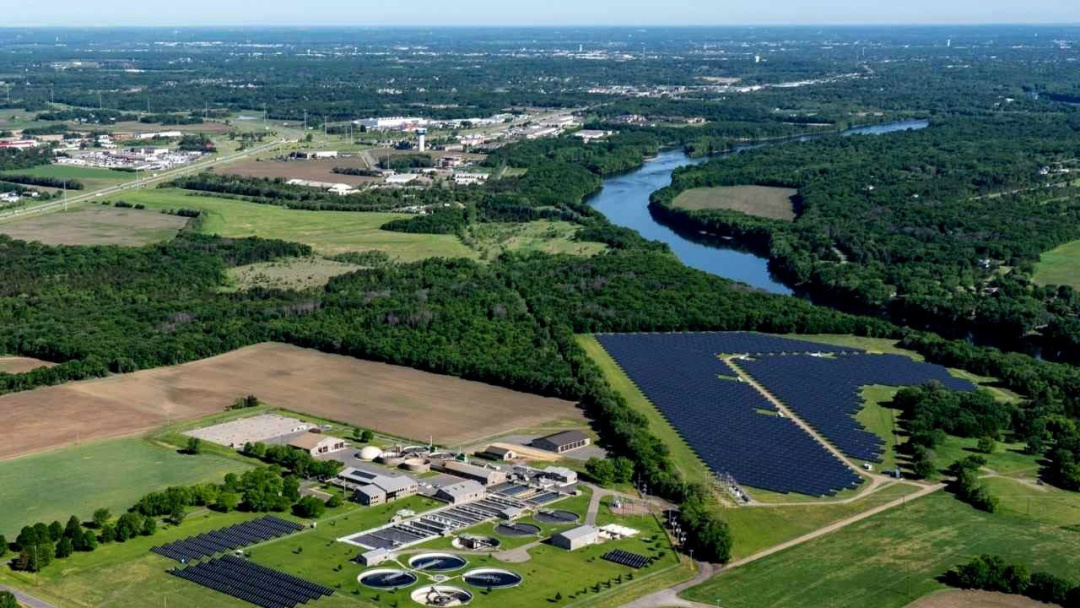
A coordinated cyberattack has affected over 30 community water systems across Minnesota and six other states, prompting federal investigations. Agencies including the FBI and CISA are looking into the incident, which is believed to involve Iranian-affiliated hackers. While some…
A coordinated cyberattack targeted over 30 community water utilities in Minnesota on July 26 and 27, prompting CISA to urge immediate action to secure programmable logic controlle…
The U.S. and Australian governments have issued guidance for critical infrastructure organizations on isolating vital operational technology systems during cyberattacks. Developed…
U.S. cybersecurity agencies, including CISA, NSA, and FBI, have issued a warning about the Laundry Bear group, linked to Russia, targeting unpatched Zimbra Collaboration servers.…
A new malware known as HollowGraph has been discovered using hijacked Microsoft 365 calendars to execute espionage activities. By embedding operator instructions and stolen files…
Cybersecurity researchers have identified a new malware named GoSerpent, which has been actively targeting government and diplomatic entities in Southeast Asia since late 2025. Di…
Researchers from Hunt.io uncovered a sophisticated cyber espionage campaign linked to Chinese actors, utilizing advanced AI tools Claude Code and DeepSeek. The campaign, identifie…
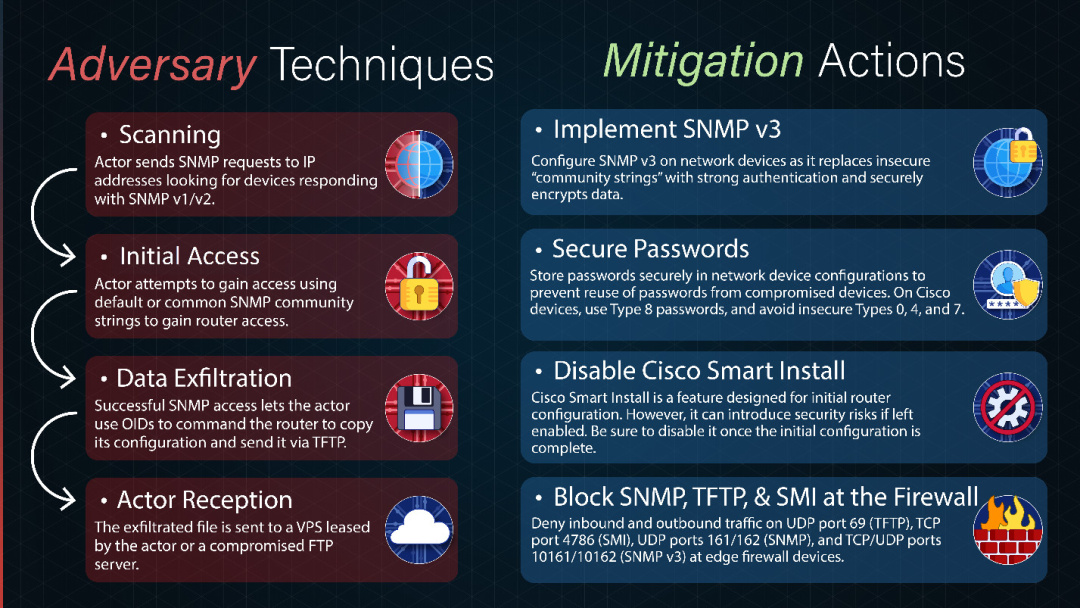
A coalition of 19 national cybersecurity agencies has issued a warning about Russian state-sponsored actors scanning the internet for routers with default or weak credentials. The…
Cybersecurity researchers have revealed a series of cyber espionage attacks against Pakistani law enforcement, particularly the Balochistan Police, attributed to threat actors ali…
Microsoft has identified a new malware known as GigaWiper, which represents a significant evolution in cyber-attack strategies. This multi-functional backdoor enables cybercrimina…
Microsoft's threat intelligence team has identified a new malware called GigaWiper, which merges features from three existing malware families into a single destructive backdoor.…
A threat group linked to China has been exploiting vulnerabilities in Roundcube webmail servers at universities in the U.S. and Canada to steal credentials and deploy malware. The…
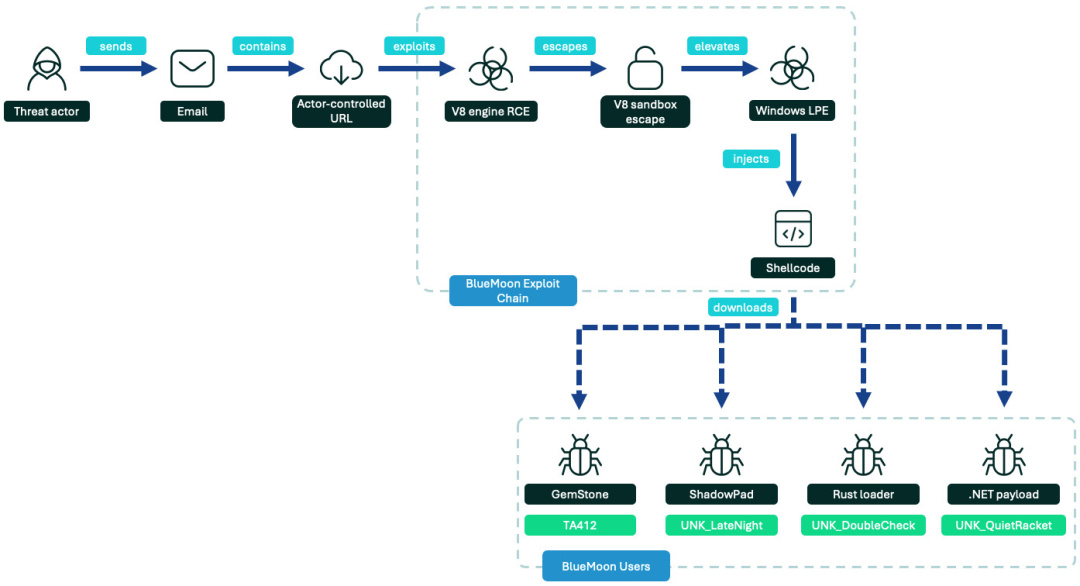
A recent report by Proofpoint reveals that four nation-state actors have utilized the BlueMoon exploit kit, which targets vulnerabilities in Chrome and Windows. This exploit kit w…
At the recent Proofpoint Protect event, industry experts discussed the evolving role of AI in cybersecurity, emphasizing the need for intent-based governance as AI agents become m…
ESET Research's latest report examines the tactics and tools employed by Gamaredon, a prominent Russia-aligned cyberespionage group, throughout 2025. The analysis highlights the g…
Microsoft has introduced its first AI-driven cybersecurity model, MAI-Cyber-1-Flash, alongside Project Perception, aimed at enhancing threat detection and response. As cyberattack…
 Spook.News