HollowGraph Malware Exploits Microsoft 365 Calendar for Espionage
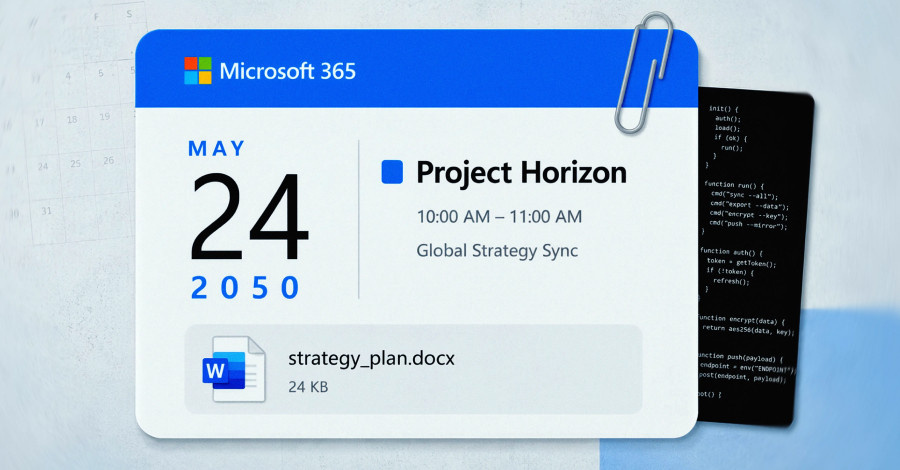
HollowGraph, a newly identified espionage malware, has been utilizing compromised Microsoft 365 calendars to facilitate its command and control operations. By embedding instructions and stolen files in calendar events set for the year 2050, the malware cleverly disguises its activities within legitimate Microsoft Graph API traffic, making it challenging for security systems to detect. Group-IB, the cybersecurity firm that uncovered HollowGraph, emphasizes that this method allows the malware to operate under the radar, as the communications appear to be standard Microsoft 365 interactions.
The malware itself is a .NET DLL that operates with only two commands: get and send. It does not connect to an attacker-controlled server for instructions; instead, it uses the compromised mailbox's calendar as a two-way dead drop. To receive commands, it queries the calendar for an event planted by the operator, which is buried in the far future, making it unlikely for the mailbox owner to notice. The malware reads instructions from an attached file and, to exfiltrate data, it encrypts stolen files and uploads them as attachments to newly created calendar events.
All data transferred through the calendar is secured with hybrid RSA and AES-256 encryption, utilizing separate key pairs for incoming and outgoing communications. Additionally, HollowGraph maintains its connection to the command infrastructure through a secondary, less sophisticated channel that refreshes the app's Entra ID login details via DNS queries. This channel operates in the clear, contrasting with the encrypted calendar traffic.
Group-IB has high confidence in linking HollowGraph to a modular backdoor framework known as Cavern, which has been associated with Iranian intelligence operations. However, the firm has refrained from naming the specific operator behind this campaign, indicating that the evidence does not allow for a definitive attribution to any known threat actor. The compromised mailbox from which data was exfiltrated belongs to an Israeli organization, but Group-IB considers this detail as geographical context rather than a direct attribution.
During their analysis, Group-IB identified the malware on at least 12 machines, with only a few actively communicating with the attackers during the observation period from June 3 to July 9, 2026. This limited activity suggests a targeted espionage effort rather than a broad opportunistic attack, despite the potential for the technique to be applied more widely.
There are no vulnerabilities in Microsoft software that can be patched to mitigate this threat, as HollowGraph exploits a compromised account and the normal functionality of the Graph API. Consequently, the focus for organizations should be on improving identity and application permissions, along with monitoring practices. Group-IB recommends vigilance in auditing client-credential OAuth apps that access Graph, as well as monitoring for unusual calendar activity, such as events created or modified by applications instead of users.
The use of trusted Microsoft services for command-and-control operations is not unprecedented, with attackers previously employing Outlook inboxes and OneDrive for similar purposes. However, the use of far-future calendar entries as a hiding place for malicious activities presents a new challenge for defenders, who may not have reason to scrutinize such entries. As the threat remains active, organizations are advised to review their Microsoft 365 environments for any suspicious calendar events, particularly those dated far into the future.








