Anthropic's latest Threat Intelligence Report reveals significant changes in cyber operations, particularly the diminishing distinction between state-sponsored and individual cyber actors. The report details how AI is being used to autonomously enhance malware and execute sophis…
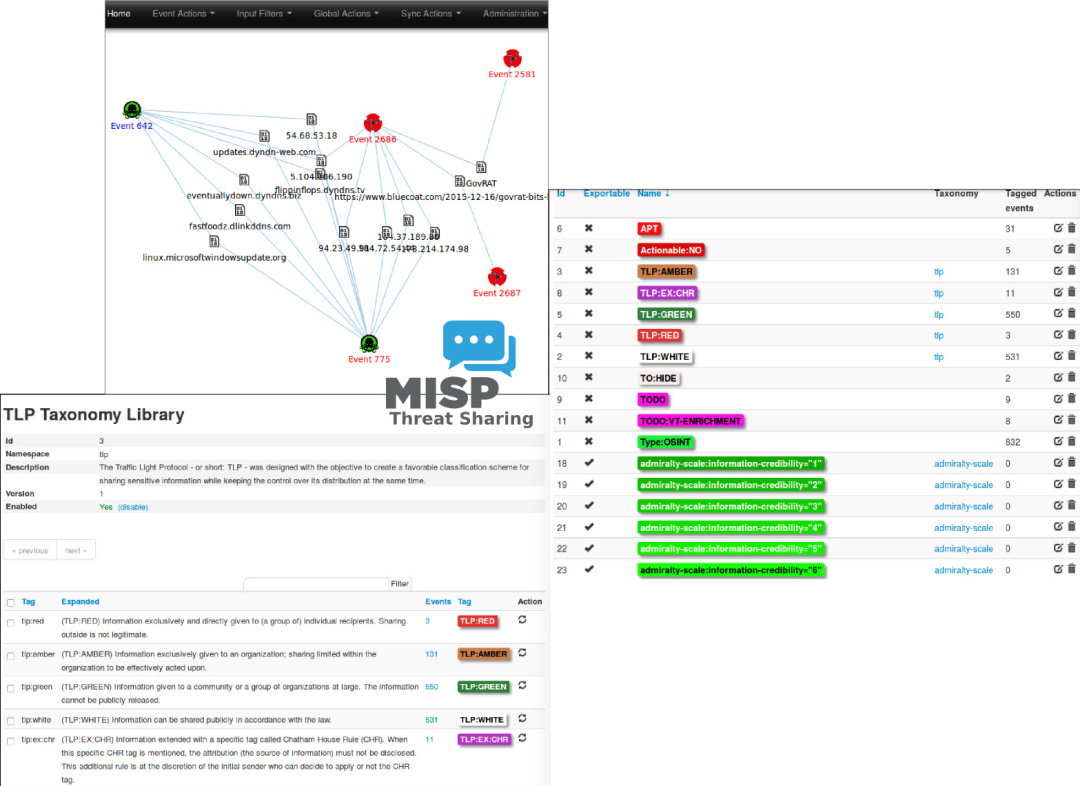
MISP v2.5.45 is an open-source platform designed for collecting, correlating, and sharing cybersecurity indicators and malware analysis. It aims to facilitate structured informati…
The FBI has successfully disrupted a proxy network that facilitated Chinese cyber espionage operations. This network, described as a technical 'quartermaster,' provided essential…
Cybersecurity researchers have identified a cyber espionage campaign, dubbed Operation QUICSILVER, which targets Myanmar's government and IT sectors. The campaign employs deceptiv…
Apollo Global Management has confirmed a data breach resulting from a social engineering attack that exposed sensitive personal information. The incident, which occurred in July,…
Google's Threat Intelligence Group has identified three Russia-linked cyber espionage clusters that exploit authentication features to compromise accounts. These groups target res…
Three suspected Russian cyber espionage groups have been identified using legitimate authentication methods to target individuals in academia, defense, and government sectors acro…
Broadcom's Threat Hunter Team has identified the Chinese APT group known as Jewelbug as being involved in both cyber espionage and lucrative cryptocurrency fraud. The group operat…
Project CAV3RN is a sophisticated espionage framework that targets Israel, utilizing Google Apps Script for command and control (C2) relays and DNS-based routing. This report deta…
Fortinet has introduced a cybercrime bounty program aimed at addressing the accountability gap in combating cybercrime. This initiative, developed in collaboration with Crime Stop…
Midnight Blizzard, a Russian hacking group linked to the country's foreign intelligence service, has been targeting public Wi-Fi networks in hotels and conference centers to steal…
Laundry Bear, a cyber espionage group linked to Russia, is exploiting a cross-site scripting vulnerability in Microsoft Exchange, identified as CVE-2026-42897, to target governmen…
The FBI has taken control of virtualine.net, a domain linked to a bulletproof hosting provider that facilitated money laundering for its criminal clientele and hosted forums for i…
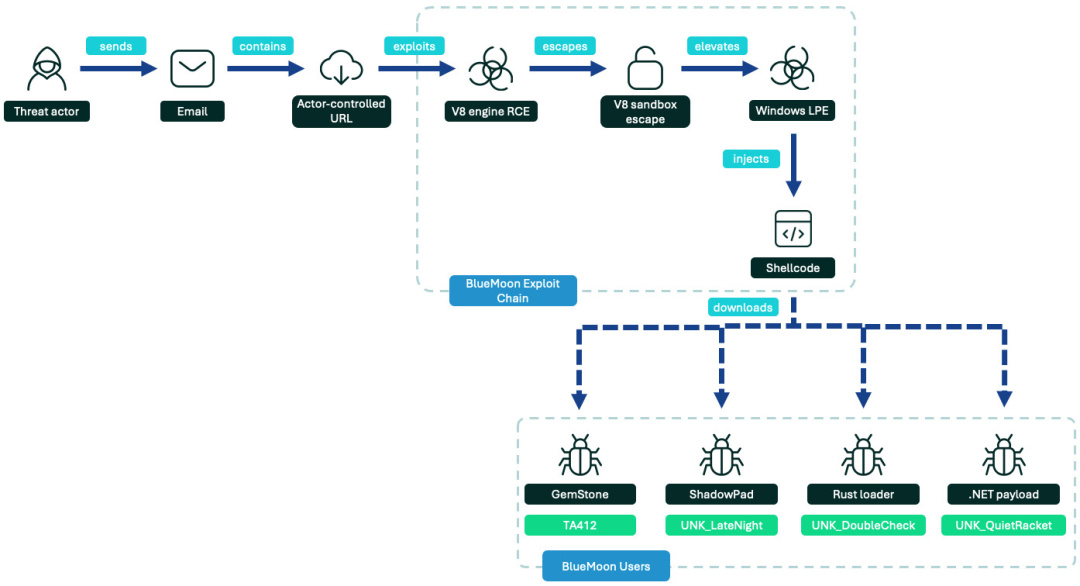
A recent report by Proofpoint reveals that four nation-state actors have utilized the BlueMoon exploit kit, which targets vulnerabilities in Chrome and Windows. This exploit kit w…
AI-linked stocks experienced a significant decline as leaders from major AI companies cautioned against the rapid advancement of artificial intelligence. This warning raises conce…
 Spook.News