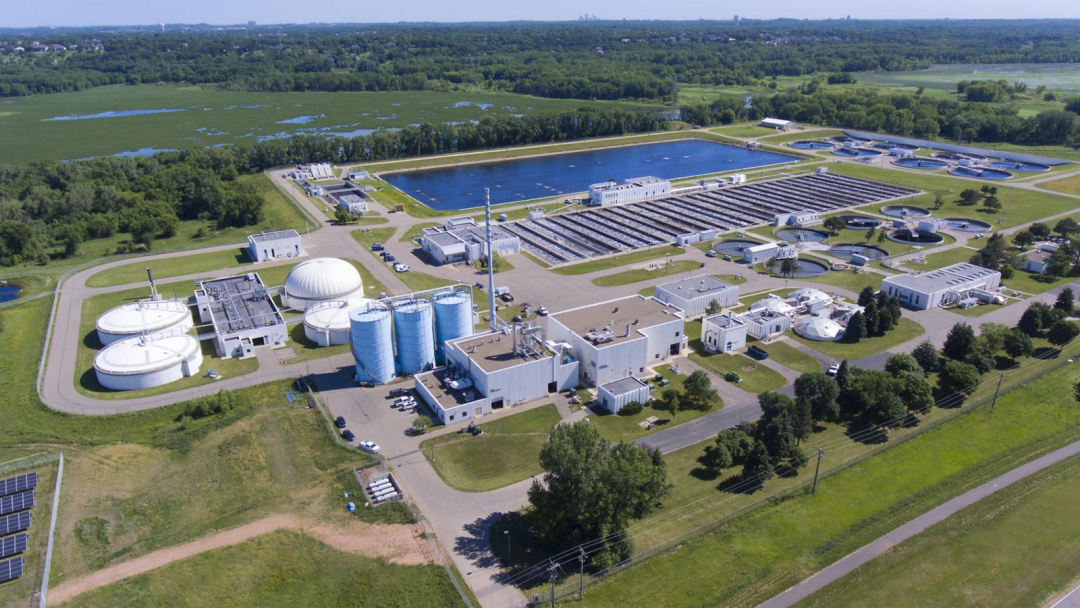
A coordinated cyberattack affected more than 30 community water systems in Minnesota on July 26 and 27, prompting a statewide cybersecurity response. Several cities reported outages and communication failures, with Braham's water plant going offline. Minnesota IT Services confir…
Minnesota IT Services has activated its cybersecurity response after hackers targeted more than 30 community water systems in a coordinated cyberattack. The attacks occurred on Ju…
Mirage Kitten, an advanced persistent threat group, has developed a new malware toolkit aimed at cyber-espionage in the aerospace, defense, and telecommunications sectors across t…
Residential proxies in the U.S. are increasingly viewed as a significant national security concern due to their role in social media manipulation and spam. These proxies operate b…
U.S. cybersecurity agencies, including CISA, NSA, and FBI, have issued a warning about the Laundry Bear group, linked to Russia, targeting unpatched Zimbra Collaboration servers.…
Microsoft has identified GigaWiper, a sophisticated malware that not only wipes hard drives but also spies on users. This multi-faceted backdoor combines features from various mal…
Recent research by Check Point reveals that artificial intelligence has evolved from a tool assisting hackers with specific tasks to a critical component in every phase of cyberat…
Microsoft has identified a new malware called GigaWiper that not only spies on data but also renders entire systems unusable. This malware can overwrite hard drives and encrypt fi…
Microsoft has identified a new malware known as GigaWiper, which represents a significant evolution in cyber-attack strategies. This multi-functional backdoor enables cybercrimina…
Microsoft's threat intelligence team has identified a new malware called GigaWiper, which merges features from three existing malware families into a single destructive backdoor.…
Talos Intelligence has identified UAT-7810, a China-linked threat actor, as actively developing new malware, including an updated version of its backdoor known as LONGLEASH. This…
Kaspersky has identified a new APT group named Armored Likho, which conducts both financially motivated attacks and targeted espionage against government and electric power sector…
The FBI has taken control of virtualine.net, a domain linked to a bulletproof hosting provider that facilitated money laundering for its criminal clientele and hosted forums for i…
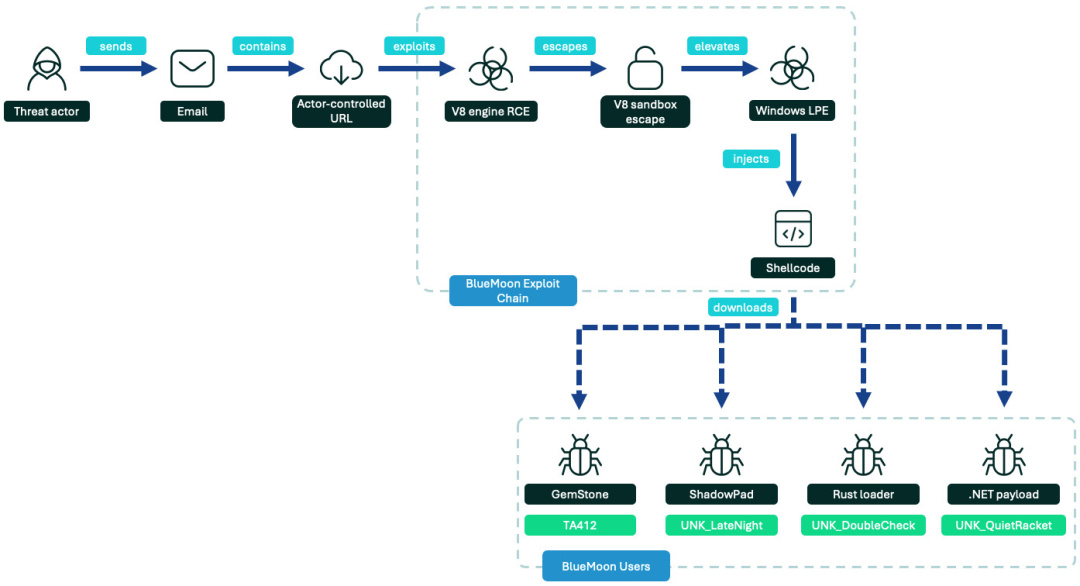
A recent report by Proofpoint reveals that four nation-state actors have utilized the BlueMoon exploit kit, which targets vulnerabilities in Chrome and Windows. This exploit kit w…
AI-linked stocks experienced a significant decline as leaders from major AI companies cautioned against the rapid advancement of artificial intelligence. This warning raises conce…
 Spook.News