Iran-Aligned Group DarkBlinders Targets Israel and Iraqi Kurdistan
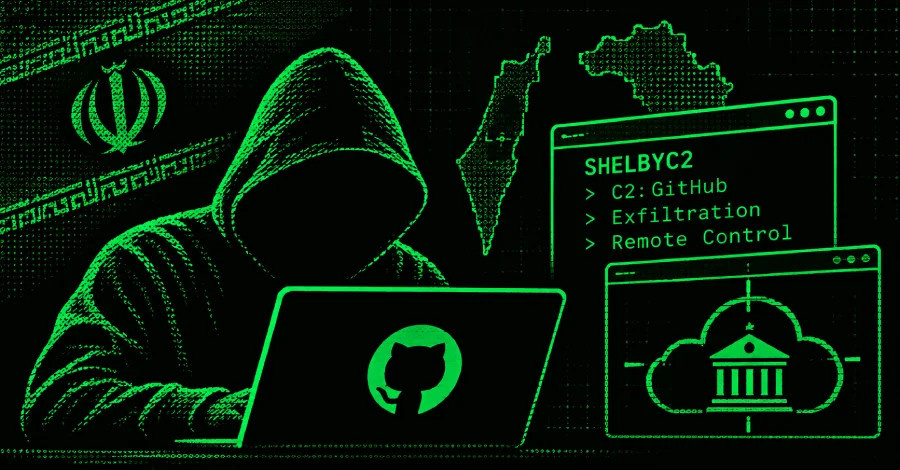
Cybersecurity researchers have disclosed a cyber espionage campaign attributed to the Iran-aligned group DarkBlinders, which targeted Israel and the Kurdistan Region of Iraq between August and October 2026. This campaign has resulted in the compromise of a high-profile individual in Israel and has also impacted a government cloud environment in the Kurdistan Region.
The DarkBlinders group has been active since at least September 2024 and is linked to previous attacks on aviation infrastructure and telecommunications in the U.A.E. and Iraq. Notably, their tactics do not overlap with those of other known hacking groups, indicating a unique operational approach.
The group's attacks primarily utilize spear-phishing as a means of initial access, enticing victims to open trojanized utilities or click on malicious links that lead to downloads of harmful software. Previous investigations by Elastic Security Labs and Group-IB have documented the deployment of SHELBYLOADER, also known as HOTAIR, which is executed via DLL sideloading to run a backdoor called SHELBYC2, also referred to as AEROSTAT. This backdoor employs GitHub for command-and-control operations, data exfiltration, and remote control.
In early October 2026, Palo Alto Networks reported on a campaign named Blinder Tunnel, where the threat actor, identified as CL-STA-1178, impersonated the Dubai Airports IT department to distribute malware-laden coding challenges to high-value targets. This recruitment scheme was first detected in late March 2026, although evidence suggests that the attackers had been preparing their infrastructure as early as November 2025.
The social engineering tactics employed by DarkBlinders involved approaching specific targets with lucrative job offers, tricking them into executing a self-contained application that mimicked a career portal. This application prompted users to complete a questionnaire, which did not exfiltrate data but served as a decoy to build credibility before delivering the actual malware payload disguised as a Microsoft Visual Studio project archive.
Techniques for Sustained Cyber Intrusion
The attack chain utilized multiple techniques to maintain persistent access, including a malicious C# project file that triggered AppDomainManager injection, followed by DLL sideloading to deliver an updated version of SHELBYLOADER. This version then launched SHELBYC2, which also deployed a tunneling utility named Blackwood.
The latest findings indicate that DarkBlinders continues to rely on social engineering, combining credential phishing with malware delivery. The group has been observed using lookalike domains for government, webmail, and cloud services to collect credentials or present malicious downloads. Among the domains identified are those associated with a fake videoconferencing application called StarkMeet, which, when installed, executes ShelbyLoader V2 and SHELBYC2.
Cleared to File
The ongoing activity of DarkBlinders suggests an evolving strategy for malware delivery, ranging from coding assessments to counterfeit software. The group is assessed to be part of a larger operational cluster that includes UNC5795 and Dust Specter, with overlapping infrastructure and malware usage. This connection highlights a shared interest in intelligence collection targeting Iraqi government entities.
As the situation develops, the emergence of new command-and-control servers associated with other Iranian threat actors, such as Prince of Persia, indicates a broader trend of cyber espionage activities linked to geopolitical tensions. The monitoring of these activities continues to reveal the complexities and challenges in countering such sophisticated cyber threats.