Volt Typhoon's Silent Train Network Disrupted After Multiple Zero-Day Exploits
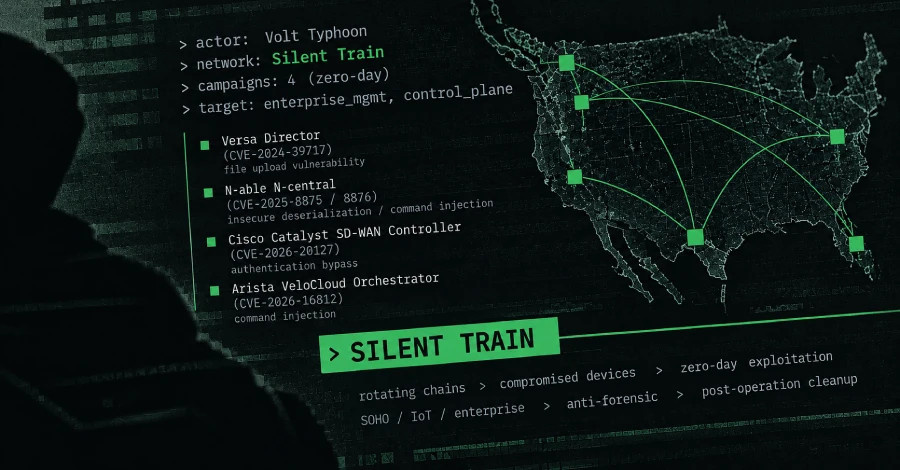
The cyber espionage group known as Volt Typhoon has been associated with a covert access network called Silent Train, which has recently been disrupted. This network was reportedly used for zero-day exploitation and strategic access to various systems. According to a report from Lumen Technologies' Black Lotus Labs, Silent Train was first identified in late 2023 and utilized rotating chains of compromised small office/home office (SOHO), Internet of Things (IoT), and enterprise infrastructure. The network employed anti-forensic techniques and compartmentalized operations to minimize detection and attribution.
Silent Train's primary function was to facilitate critical phases of cyber attacks, such as vulnerability exploitation, credential access, and data exfiltration, while ensuring continued access to victim environments. The report highlights that hundreds of victims have been identified across various sectors, including telecommunications, government, defense contractors, and critical infrastructure services like water and energy.
Volt Typhoon, also known by several other names including Bronze Silhouette and Vanguard Panda, has been active since at least 2021. The group has previously exploited vulnerabilities, such as a zero-day in Versa Director, to deploy a web shell designed to harvest credentials. Recent findings indicate that Silent Train was involved in four confirmed zero-day campaigns, with one of these vulnerabilities impacting over 30 victims.
Silent Train's Covert Operational Tactics
The operational model of Silent Train involved rapidly rotating chains of compromised devices, which were exploited on demand against carefully selected targets. This approach allowed Volt Typhoon to maintain operational security while minimizing opportunities for detection. The network's activity surged following the disruption of the KV-botnet, which is linked to multiple state-sponsored threat actors, including Volt Typhoon.
Intelligence Reviewed
By early 2025, Silent Train evolved from a completely ephemeral relay network to a hybrid architecture, retaining enterprise-grade devices for longer periods. The network's design allowed for the relaying of malicious traffic through multiple devices, obscuring its origins from both victims and defenders. This operational discipline focused on short-lived sessions rather than persistent infrastructure, further complicating attribution efforts.
The states of Hawaii, California, and Texas have emerged as focal points for Silent Train operations, as they host significant military and telecommunications infrastructure. The targeting of these areas indicates a deliberate strategy to maintain access to critical ecosystems that support defense and logistics operations, particularly during heightened tensions in the Indo-Pacific region. The structured framework of Silent Train illustrates how Volt Typhoon systematically pursues and preserves access to crucial networks in the United States.