Cyberattack Forces European Governments to Take Websites Offline Due to PHP Flaw
Government websites and online services across Europe were taken offline recently due to critical vulnerabilities in the widely used PHP programming language. This prompted a global security response as cybersecurity experts alerted operators that hackers could exploit these flaws on a large scale. In light of the situation, PHP developers released security patches and urged users to update their systems immediately. Technology firms reported that attackers were already attempting to exploit these vulnerabilities, leading many organizations to temporarily shut down their websites as a precaution.
The vulnerabilities were discovered by two cybersecurity companies, Calif and Wiz, which utilized artificial intelligence in their research. Calif identified the flaws using a large language model, while Wiz employed its autonomous AI vulnerability research tool. These vulnerabilities had remained hidden in PHP's codebase for over a decade, making them particularly difficult for human hackers to exploit at scale. Experts noted that the advent of AI has significantly lowered the barriers to identifying and exploiting such vulnerabilities.
As the situation unfolded, Amazon's security team detected an attempt to exploit the vulnerabilities against one of its decoy systems just days before the public disclosure. This attempt, originating from an anonymous internet address, raised concerns about how the attackers had gained knowledge of the vulnerabilities while they were still under embargo. Following the public announcement, multiple actors made further attempts to exploit the flaws, indicating that they were being broadly targeted.
Global Impact of PHP Vulnerabilities
The PHP vulnerabilities pose a significant global risk, as PHP is a programming language that powers approximately 75% of websites that can be identified by their programming language. This includes popular platforms like WordPress, Drupal, and Joomla. Cybersecurity agencies have urged website operators to apply the patches immediately or take their websites offline until the fixes can be installed. Smaller websites, particularly those run by individuals or organizations with limited technical resources, are at greater risk.
Final Brief
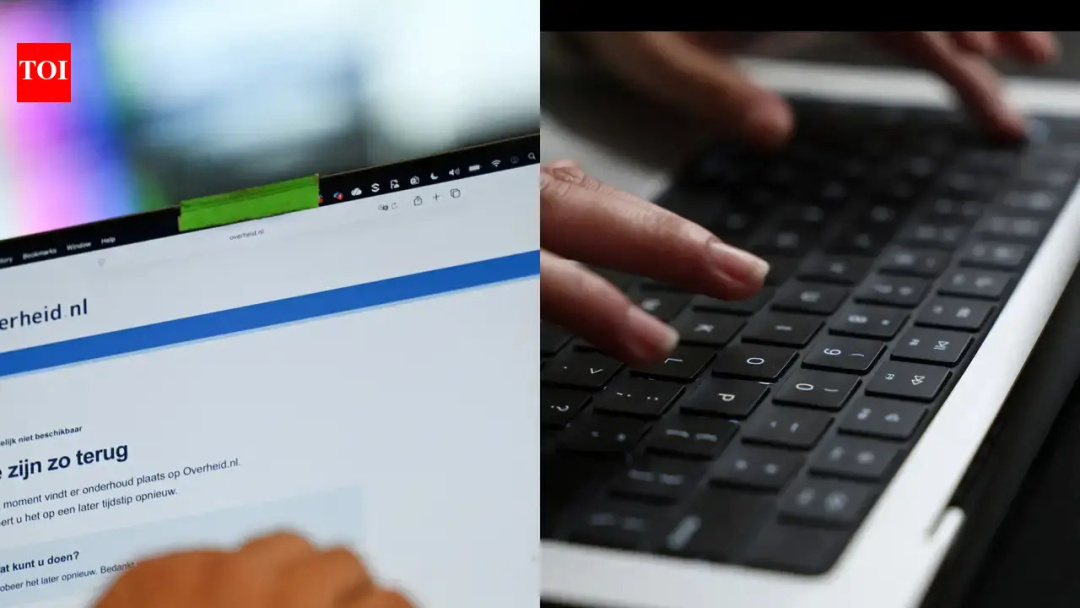
In response to the vulnerabilities, several European countries initiated precautionary shutdowns. The Netherlands' National Cyber Security Centre went offline, followed by various organizations, including the Port of Rotterdam and government portals. In Denmark, a municipal IT company shut down several services, while Finland's state IT services provider took public network services offline as a precautionary measure. The French Interior Ministry also placed all its websites under preventive maintenance.
As the situation continues to evolve, experts warn that AI-assisted hacking campaigns could lead to widespread disruption if vulnerable servers remain unpatched. The urgency of addressing these vulnerabilities is underscored by the potential for mass exploitation, which could compromise a significant portion of the internet.