Spear-Phishing Campaign Targets Taiwan Research Affiliates Using AitM Techniques
Cybersecurity researchers have disclosed details of a spear-phishing campaign conducted by an advanced persistent threat (APT) group, which has specifically targeted individuals affiliated with research organizations in Taiwan. This campaign directs victims to an adversary-in-the-middle (AitM) phishing framework designed to harvest their Google account credentials and multi-factor authentication (MFA) codes.
The activity is tracked by Cisco Talos under the designation UAT-11985, which suggests that the operation is likely supported by artificial intelligence (AI) to generate tailored phishing lures aimed at various targets within a common social engineering framework. The campaign was first observed in mid-2026.
According to Talos researcher Joey Chen, the operation has leveraged legitimate public event themes and impersonated reputable academic and policy institutions to establish credibility. This approach enhances the likelihood of success by making the phishing attempts appear more legitimate.
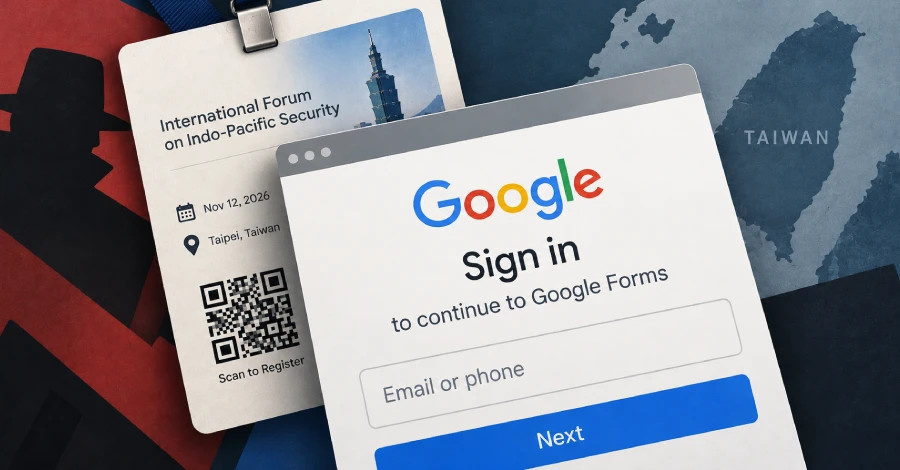
In addition to traditional email phishing tactics, the attackers have incorporated QR code phishing, or 'quishing,' techniques. They modify legitimate event posters to include malicious QR codes, thereby expanding the attack surface beyond just email recipients to include secondary victims who may encounter printed materials.
Central to the operation is the use of credible public event information in spear-phishing emails, which contain URLs pointing to attacker-controlled infrastructure. When hovering over these hyperlinks, they display a legitimate-looking Google Forms URL, further deceiving potential victims.
Patterns in Phishing Email Construction
The phishing emails exhibit a consistent syntactic structure, despite covering a wide range of geopolitical topics. This indicates that the content was mass-produced from a reusable prompt template rather than being meticulously crafted for each individual target.
The threat actor has been found to impersonate legitimate Taiwan-based institutions, such as the Taiwan European Union Centre and the NCCU Institute of International Relations, fabricating sender identities to enhance the messages' credibility. Talos noted that the combination of a nearly identical narrative structure, rhetorical style, personalized flattery, institutional impersonation, and deceptive registration mechanisms strongly suggests a coordinated and carefully targeted spear-phishing campaign.
In some instances, the phishing emails have included legitimate event posters scraped from authentic websites, but with the QR codes altered to mislead victims into scanning them to 'register' for the event. The phishing site mimics a legitimate Google Form, but its primary goal is to prompt victims to sign in with their Google accounts to complete the form. This process leads them to a counterfeit site featuring a spoofed Google login panel designed to capture their credentials and authentication challenges.
Intelligence Reviewed
The replica site functions as an AitM proxy, utilizing obfuscated JavaScript to collect and exfiltrate the entered information in real-time over a WebSocket connection, while simultaneously forwarding it to legitimate Google authentication servers. Prior to establishing this connection, the JavaScript payload gathers device and browser information, which is reported to the command-and-control (C2) server.
The phishing panels only support Simplified Chinese, Traditional Chinese, and English locales, with region detection based on the victim's browser settings, indicating a specific targeting of Chinese-speaking users. By splitting one-shot uploads with POST requests from low-latency state updates via WebSocket, the threat actor has engineered a seamless credential-harvesting relay, allowing for full account takeover without raising suspicion among victims.