Italy's Foreign Ministry Faces Cyberattack Amid Embassy Site Reviews
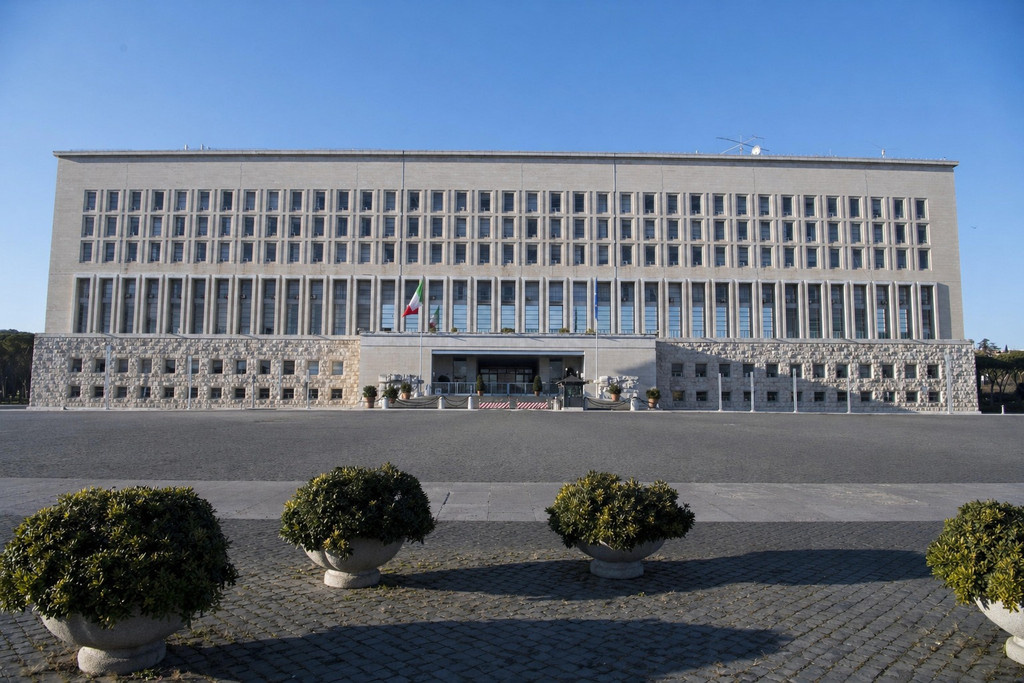
On October 8, 2026, Italy's Ministry of Foreign Affairs announced that its website was experiencing a cyberattack. According to the ministry, its protective systems have successfully mitigated the attack thus far, with no reported disruptions. The ministry has not disclosed the identity of the attackers or the nature of the cyber threat.
The ministry is actively monitoring the situation in collaboration with the Polo Strategico Nazionale, Italy's national cloud hub, and relevant authorities. Foreign Minister Antonio Tajani emphasized that cybersecurity is a key component of the reforms implemented within the Foreign Ministry over the past year. He noted that Italy has enhanced its capabilities to prevent, monitor, and respond to cyber threats, including adopting necessary technological countermeasures.
Tajani also highlighted discussions with German Foreign Minister Johann Wadephul regarding the technical capabilities of the CSIRT Operations Room during a recent visit to Rome. In light of the ongoing cyber threats, Italy is working with Romania and other EU member states to propose measures in upcoming European meetings aimed at identifying those responsible for cyberattacks targeting Italian institutions.
Analysts are currently assessing the websites of Italian embassies and consulates abroad for similar cyber threats. This scrutiny is crucial, as any disruption to embassy websites can significantly impact citizens abroad who rely on these sites for essential services and information.
Past Cyberattacks and Future Strategies
The Foreign Ministry has faced similar challenges in the past. In December 2024, Russian hackers reportedly took down its website, which was restored the following day. DDoS attacks, which primarily affect website availability rather than data integrity, can create significant public concern, especially when they target government institutions.
The ministry's proactive measures include strengthening technical defenses and advocating for EU-level proposals to hold cyberattack perpetrators accountable. This approach aims to deter future attacks by making attribution more challenging for potential aggressors.
Cleared to File
While DDoS attacks can disrupt services and attract media attention, they are often not complex operations for a well-prepared state to counter. Authorities must discern whether these attacks are merely disruptive actions or if they serve as distractions for more sophisticated cyber operations occurring simultaneously. Understanding the intent behind such attacks is essential for effective cybersecurity strategy and public communication.
The narrative surrounding cyberattacks can amplify perceived threats, leading to public fear and uncertainty. Governments face the challenge of defending against these disruptions while ensuring that the actual impact of such attacks is accurately communicated to the public. The risk lies not only in the attack itself but also in the potential for misinformation regarding the severity of the threat.