TA419 Cyber Espionage Group Targets U.S. AI Experts with Phishing Attacks
A new cyber espionage group known as TA419, aligned with China, has been linked to a series of credential phishing campaigns targeting artificial intelligence (AI) experts in the United States. These campaigns have specifically focused on individuals working for think tanks, universities, and legal organizations. The attackers have impersonated prominent economists and AI policymakers, including a notable employee from Anthropic, to target an AI policy expert at a U.S. think tank in February 2026. The phishing emails often carried subject lines such as "Request for Feedback on Military Integration of Claude."
According to an analysis by Proofpoint, this activity likely supports broader Chinese intelligence objectives aimed at understanding developments within the U.S. AI policy and regulatory landscape. This comes at a time of heightened strategic competition between the U.S. and China, marked by accusations of model distillation and export controls. Proofpoint has characterized TA419 as a threat actor motivated by espionage, with a history of orchestrating credential phishing campaigns against individuals associated with U.S. and Japan-based think tanks, defense contractors, universities, and law firms since at least April 2025.
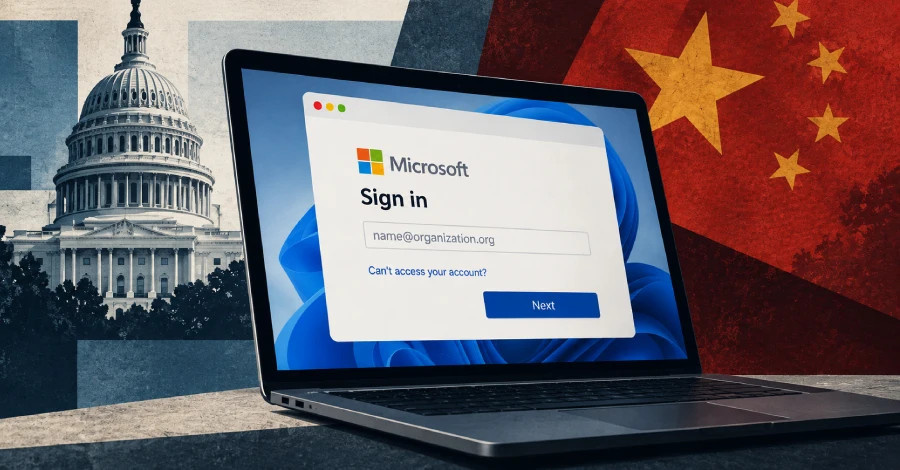
In July 2026, the group reportedly impersonated several individuals, including a former member of the White House Office of Science and Technology Policy, as part of its phishing efforts targeting AI policy experts in the U.S. The initial outreach often appears harmless, designed to build trust with the target. Once the recipient engages, the attackers follow up with a shortened URL that leads to a multi-stage redirection chain, ultimately directing the victim to an OneDrive adversary-in-the-middle (AitM) credential phishing page after passing a Cloudflare Turnstile check.
The phishing page employs a technique known as Frameless BitB, a variant of the browser-in-the-browser (BitB) attack. This method creates a fake browser window within a legitimate browser session using HTML, CSS, and JavaScript, allowing the attackers to spoof trusted websites or login pages. Unlike traditional BitB attacks that utilize iframes, Frameless BitB achieves its goals without them, relying on script injections and HTML/CSS tricks to create a convincing visual effect.
Advancements in Phishing Techniques Revealed
Proofpoint notes that TA419 has enhanced its phishing toolkit with a custom telemetry and automation module that tracks the target's Microsoft sign-in flow. This module captures credential information using the AitM proxy while relaying the details to the actual Microsoft infrastructure in the background. The primary advantage of this method is that victims remain unaware of any wrongdoing, as the sign-in event appears successful, and there are no signs that session cookies have been covertly captured.
Cleared to File
To mitigate the risks posed by TA419, organizations are advised to implement phishing-resistant authentication methods, such as passkeys. Individuals targeted by TA419 should exercise caution when responding to unsolicited outreach and verify the authenticity of such communications before proceeding.
Proofpoint emphasizes that TA419 has consistently targeted sectors related to defense, national security, energy, international relations, and foreign policy, primarily focusing on connections to the U.S. and Japan. The targeting of AI policy experts represents a continuation of this focus rather than a shift in strategy.