Jewelbug: China-Linked Group Conducts Cyber Espionage and Cryptocurrency Fraud
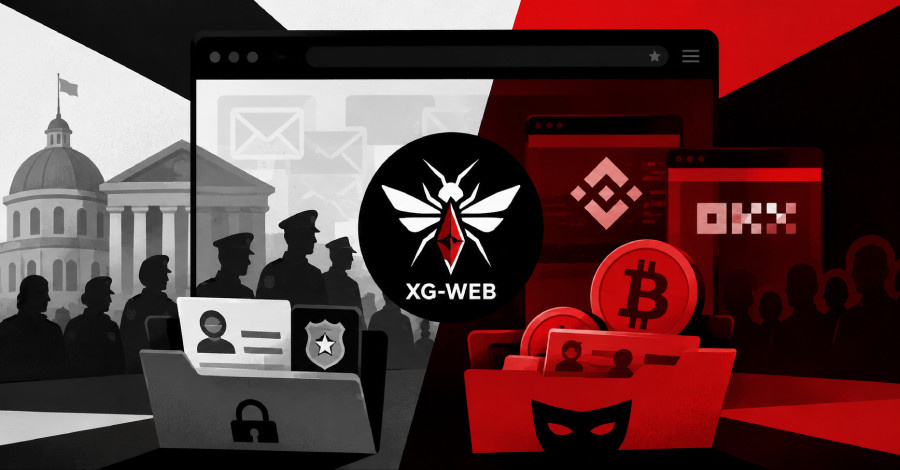
Jewelbug, a cyber threat actor associated with China, has been identified as conducting cyber espionage operations aimed at governments and military organizations, alongside a parallel operation focused on cryptocurrency fraud. This dual approach is managed through a single control panel known as XG-Web, which serves as a browser-centric remote-access and information-stealing framework. This tool effectively transforms a victim's browser into a remote-control channel, allowing the group to infiltrate internal networks.
The group is believed to operate as a hackers-for-hire entity, targeting various regions including the Middle East, Southeast Asia, and South Asia. Their operations involve five generations of command-and-control code and a suite of implants that span across different platforms, including browsers, Windows endpoints, and Linux servers. This comprehensive toolset is designed to facilitate both espionage activities and cryptocurrency fraud, particularly aimed at Chinese-speaking victims.
Recent investigations by Broadcom's Symantec and Carbon Black Threat Hunter Team have revealed extensive espionage campaigns targeting government organizations, with over 90 email addresses from police and government entities in South Asia being compromised. The group's operations also include a sophisticated Linux and router implant that extends their reach into network infrastructures, with some builds configured to communicate through the internal corporate proxies of major U.S. companies.
In addition to espionage, Jewelbug has been linked to fraudulent activities targeting cryptocurrency users. They employ deceptive tactics, including fake exchange-download portals, to lure victims into downloading malicious software. The presence of decoy documents that impersonate Taiwanese government entities indicates a broader targeting strategy that likely includes Taiwan.
Central to Jewelbug's operations is the XG-Web platform, which is built on a React panel and utilizes a Node.js backend with a MySQL database. This platform is designed to conduct penetration testing while regularly checking its command-and-control infrastructure against VirusTotal for rapid updates. The group also uses public Google Docs to host obfuscated payloads, ensuring that their malicious activities remain concealed.
One of the primary tools used by Jewelbug is a malicious browser extension named "PDF Viewer," which is compatible with both Google Chrome and Mozilla Firefox. This extension requests extensive permissions to access sensitive data, allowing it to harvest credentials and monitor user activity across various websites. Notably, it includes a clipboard module that can swap cryptocurrency wallet addresses, although this functionality has not been observed in recent campaigns.
Jewelbug's operations have been characterized by significant scale, with reports indicating the collection of over one million implant check-ins, 580,000 stolen browser cookies, and thousands of captured credentials. Their financial operations are reportedly run through a registered Chinese company that masquerades as a search engine optimization service, but is actually involved in an SEO poisoning scheme designed to mislead users into downloading malicious software.
The findings underscore the increasingly blurred lines between state-sponsored cyber espionage and traditional cybercrime, highlighting Jewelbug's unique position as a hack-for-hire group capable of executing both espionage and financial fraud from the same infrastructure. This dual mission exemplifies the evolving landscape of cyber threats, where nation-state actors and criminal enterprises often overlap in their tactics and objectives.