Data Breach Exposes Contact Details of UK Police and Justice Staff
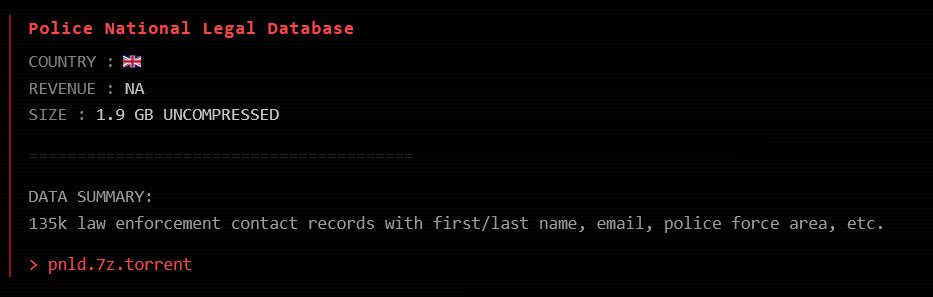
The Police National Legal Database (PNLD) has confirmed a significant data breach that has exposed the contact details of police officers, staff, and criminal justice professionals. This sensitive information, which includes names, organizations, and work email addresses, has reportedly been published on the dark web. The breach also impacted Ask the Police, a public Q&A service hosted on the same platform. The National Crime Agency (NCA) is currently involved in the investigation of this incident.
According to the PNLD's notice, there is no evidence suggesting that passwords or other security credentials were compromised. However, the exposure of names and email addresses raises concerns about targeted phishing attacks against police officers and the public who have submitted inquiries to Ask the Police. The PNLD has not disclosed the exact number of individuals affected by the breach, nor has it provided a timeline for when the intrusion occurred or how much data was taken.
The PNLD reported 108,429 police registrations in its 2025-26 annual summary, indicating a potentially large user base affected by this breach. The notice emphasized that the data security incident primarily impacted the PNLD, which also hosts the Ask the Police site. As a result, names and email addresses of individuals who previously submitted questions to the service have been made visible on criminal forums.
PNLD provides legal information and services to UK police forces and criminal justice organizations but does not store confidential information related to victims, witnesses, or offenders. All organizations affected by the breach have been promptly notified and provided with guidance. The incident has also been reported to the UK Information Commissioner’s Office (ICO).
On July 26, the extortion group ExfilSquad listed PNLD on its leak site, although PNLD has not confirmed any direct attribution to this group. Cybersecurity firm VenariX analyzed samples from 11 of ExfilSquad’s claimed victims and found similarities indicating a possible campaign pattern involving misconfigured Microsoft Power Pages portals. These public-facing sites can expose data if overly permissive access settings are in place.
PNLD’s 2023-24 annual summary noted that the database utilizes Microsoft Power Platform technology, and the breach notice referenced assets on Microsoft’s content.powerapps.com domain, supporting the connection to Microsoft’s platforms. However, neither PNLD’s notice nor VenariX’s report has confirmed a specific endpoint or access route related to the breach, leaving the Power Pages hypothesis as a plausible but unverified explanation.
VenariX stated that the reviewed data appears to have been extracted from public Microsoft Power Pages portals configured to allow anonymous users to read Dataverse records. They recommend that organizations using Microsoft Power Pages review their table permissions and settings to prevent unauthorized data access. Microsoft offers controls to block unauthenticated users from reading Dataverse data while still allowing public submissions, a configuration that should have been validated prior to deployment.
Police officers and staff whose details were compromised are advised to remain vigilant against targeted phishing attempts that may use their names, organizations, and work emails, which are now accessible on the dark web.