Ukraine and FBI Uncover Russian Cyber Campaign Targeting Messaging Accounts
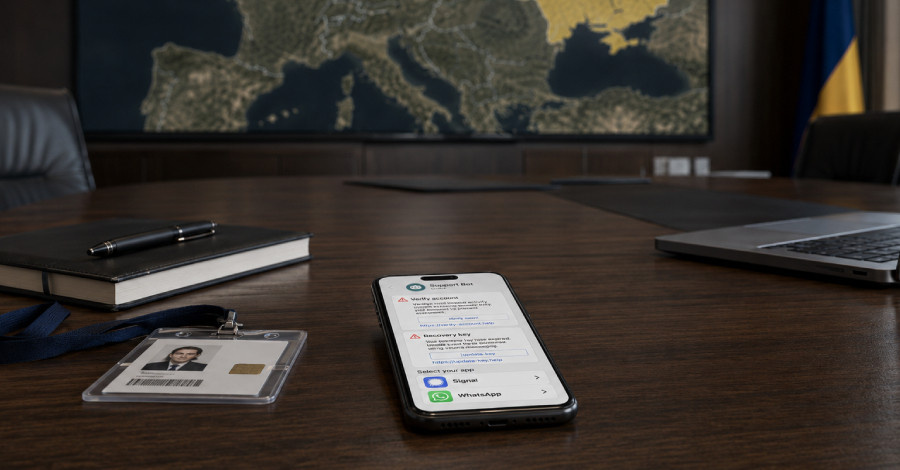
The Security Service of Ukraine (SSU), in collaboration with the U.S. Federal Bureau of Investigation (FBI), has uncovered a sustained cyber campaign orchestrated by Russian intelligence aimed at infiltrating the messaging accounts of government officials, military personnel, politicians, and activists across Ukraine, Europe, and the United States. This operation seeks to extract sensitive information, including military, political, and economic data, as well as personal details from the victims.
The attackers employ a tactic of sending SMS messages that impersonate the messaging platform's support bot, prompting users to disclose their account credentials. The SSU has indicated that these cyber attacks are not limited to public figures; they also target personal accounts of Ukrainian citizens. While the campaign has not been directly linked to a specific hacking group, similar attacks on users of messaging apps like Signal and WhatsApp have been associated with Russian threat activity clusters known as Star Blizzard, UNC5792 (also referred to as UAC-0195), and UNC4221 (also known as UAC-0185).
In light of these threats, the SSU advises users to regularly review their active messaging app sessions, log out of any unknown connections, enable two-factor authentication, and avoid scanning QR codes from unknown sources. Users are also urged not to share confirmation codes, PINs, passwords, or recovery keys, and to exercise caution when clicking on links or opening files from dubious chats.
This revelation coincides with the FBI's attribution of ongoing phishing campaigns to Russian Intelligence Services (RIS), targeting high-value individuals through commercial messaging applications to extract backup recovery keys. Additionally, the Computer Emergency Response Team of Ukraine (CERT-UA) recently linked a spear-phishing campaign aimed at government organizations to the Belarus-aligned threat actor known as UNC1151 (also called Ghostwriter and UAC-0057), which utilized compromised accounts to deploy an information-stealing malware named OYSTERBLUES.