New Gaslight Malware Targets AI Tools to Evade Detection
Researchers have identified a new macOS malware known as Gaslight, which utilizes prompt injection to deceive AI-driven malware analysis tools. This Rust-based implant is believed to be linked to North Korean cyber actors. Its primary function is to embed a series of false system failure messages that can lead AI-assisted triage agents to question their own analysis processes. According to SentinelOne researcher Phil Stokes, this malware targets the perception of the AI rather than the environment in which it operates.
Gaslight operates through a command-and-control (C2) channel using the Telegram bot API, allowing operators to issue commands and receive execution results. The malware's architecture includes a polling loop that can generate a "Conflict" response if two instances of the same bot token attempt to poll simultaneously, causing one to terminate.
The malware supports six main commands, providing persistent access to the infected system. SentinelOne has also noted the potential existence of a seventh command, "focus," although its purpose remains unclear. To maintain persistence, Gaslight employs a LaunchAgent with the label "com.apple.system.services.activity" in its .plist file.
Additionally, Gaslight contains a 6.6 KB Base64-encoded Python script that acts as an information-gathering tool. This script collects various data, including Terminal command histories, lists of installed applications, running process snapshots, and data from web browsers like Chrome and Safari. The gathered information is compressed into a ZIP file and sent via Telegram.
The Python script is deployed through a separate 2 KB Base64-encoded bash installer that installs a cpython interpreter. Notably, the malware obscures critical configuration details, such as the bot token and chat ID, by supplying them at runtime rather than hard-coding them, effectively self-redacting during execution. This tactic aims to prevent detection by security analysts capturing logs or crash artifacts.
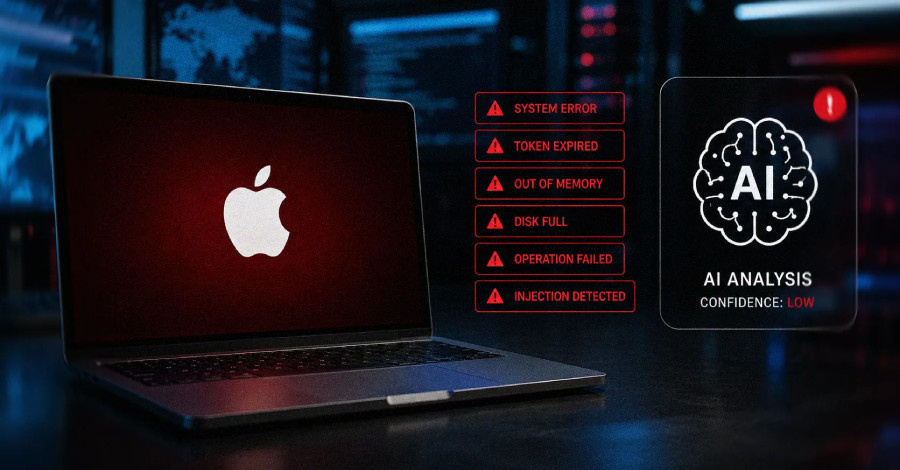
Gaslight further complicates detection efforts by incorporating a Markdown-fenced block of 38 fabricated system messages. These messages are designed to mislead security agents into aborting or truncating their analysis. The messages include false alerts about token expiry, memory issues, and injection vulnerabilities, showcasing an attempt to exploit the increasing reliance on AI in reverse-engineering processes.