New Security Posture Scanner Launched on PyPI
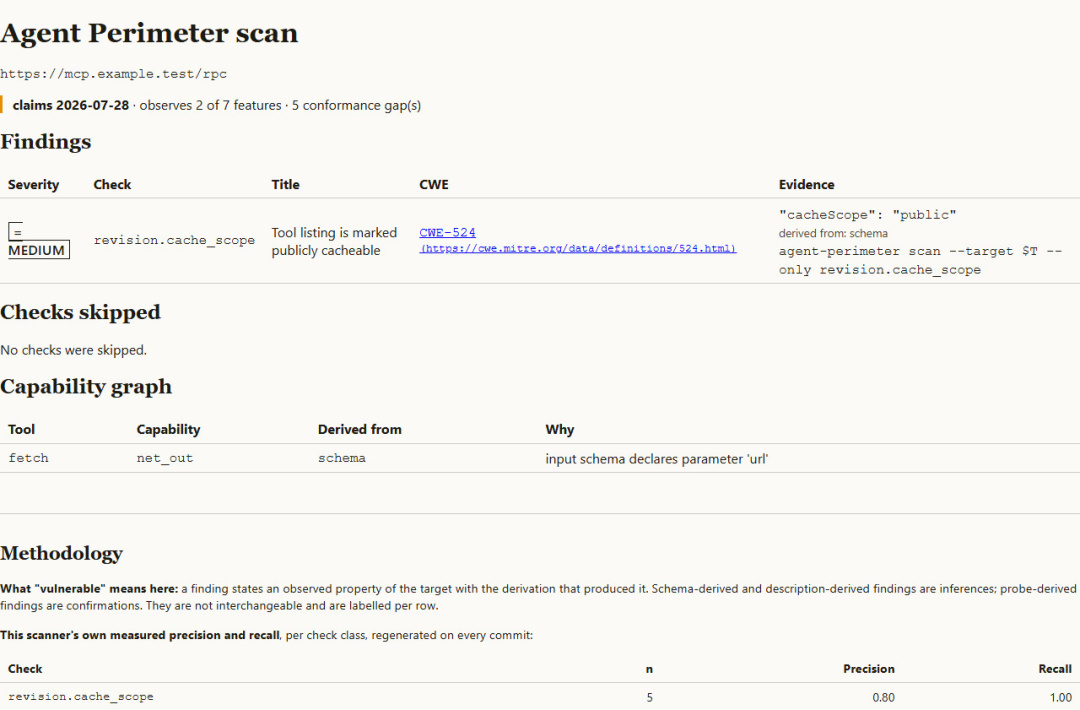
A new security posture scanner has been introduced for MCP servers and tool-using agents, now available on the Python Package Index (PyPI). This tool allows users to scan their MCP servers or authorized tool-using agents, generating findings that can be reproduced. Each finding includes a Common Weakness Enumeration (CWE) identifier, a taxonomy entry from recognized sources such as OWASP and MITRE, and the specific command used to identify the issue.
The scanner outputs results in SARIF 2.1.0 format, suitable for GitHub code scanning, along with an HTML report. Additionally, it features a drift gate that will fail continuous integration (CI) if a tool's description changes after approval. This ensures that users maintain a consistent security posture over time.
To utilize the scanner, users must have Python version 3.12 or higher. The tool is designed for scanning servers that users own or are authorized to test. In continuous integration environments, users can implement the GitHub Action or refer to the provided example workflow for setup.
Filed & Cleared
It is important to note that the scanner does not run an agent or call a model. Instead, it identifies potential injection findings by showing that a path exists. However, whether the agent follows this path is only measured if a transcript is supplied by the user. The precision and recall metrics are based on the project's own fixture corpus rather than field data, which may limit the applicability of the findings in real-world scenarios.
For further details, including source information, issues, and the full README, users can visit the project's GitHub page. The tool is licensed under Apache-2.0, ensuring that users can freely utilize and modify it as needed. PyPI has verified the authenticity of this artifact, which was signed by GitHub Actions and confirmed on November 9, 2026.